Prompt Injection
Instructions cross a trust boundary.
Enterprise AI Security & Assurance
Orbyntis helps CIOs, CISOs, and technology leaders make agent authority visible, controls testable, and every critical action reviewable.
 SAP Systems
AUTONOMOUS AI ASSURANCE
Test agent authority before critical actions reach production.
Explore AgentShieldAUTONOMOUS AI ASSURANCE
Keep the evidence behind every reviewable decision.
Explore Evidence VaultAUTONOMOUS AI ASSURANCE
Turn policies into explicit permissions and operating limits.
Explore GovernAUTONOMOUS AI ASSURANCE
Bring assurance checks into the software delivery workflow.
Explore CI GateAUTONOMOUS AI ASSURANCE
Observe agent activity and control runtime risk.
Explore Runtime GuardApproved Technology Partners

Explore one architecture through 15 private, in-browser questions.Directional, not a certification.
Guided Exposure Check
Answer from the perspective of the highest-impact agent you operate or plan to deploy.
Directional Exposure Index
Threat Exposure Map
Select any combination. The map shows exposure paths to review—it does not claim that a selected platform is vulnerable.
Select a platform or capability to begin.
Instructions cross a trust boundary.
External content influences agent behavior.
A valid tool is used outside intended purpose.
Actions change systems without a sufficient gate.
Sensitive context reaches an unintended destination.
Stored context changes later decisions.
Delegated authority exceeds the initiating scope.
Action ownership becomes ambiguous.
Agent rights exceed least privilege.
Policy behavior is intentionally bypassed.
External models, tools, or content alter trust.
Server authorization and tool scope need review.
Tool metadata or behavior becomes hostile.
Critical actions cannot be reconstructed.
Three questions matter before an autonomous system reaches production.
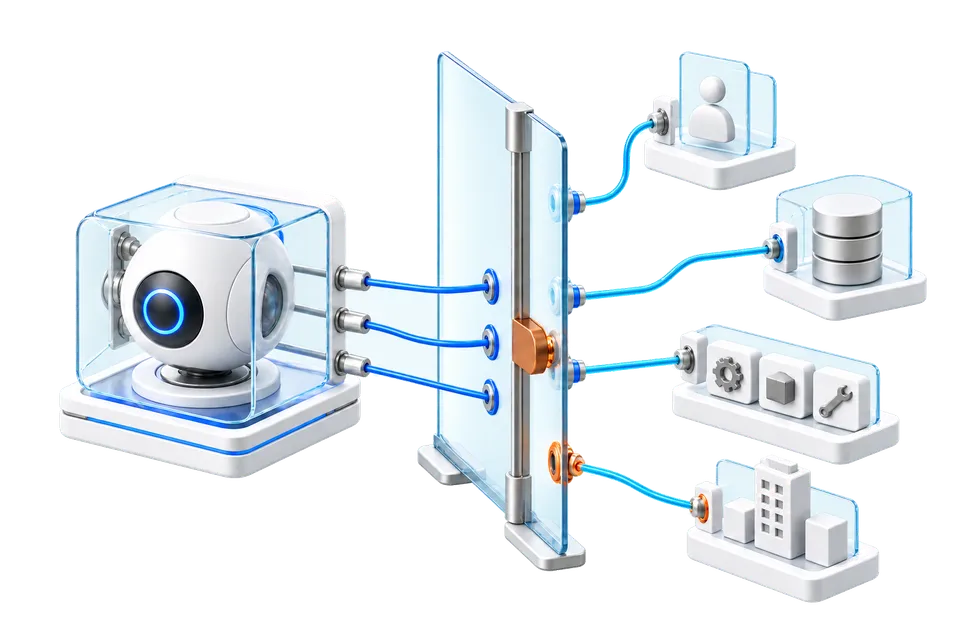 Know the boundaryWhat may the system access, decide, and change?Map what the system may access, decide, and change.Learn More
 Test the pressureWhere can misuse paths bypass the intended control?Exercise misuse paths before they become operational incidents.Learn More
 Prove the controlWhat evidence proves the action stayed accountable?Leave reviewable evidence for engineering and governance teams.Learn More
Start with the risk you need to understand. Expand only when you are ready.
Assess exposure before AI acts.
Map permissions, tools, memory, identity, and action boundaries--then test where control can fail.
Explore AgentShield
Keep assurance evidence reviewable.
Organize the evidence created through assessment, validation, and operational review.
Explore Evidence Vault
Make ownership and approval explicit.
Connect AI actions to clear decision rights, review points, and accountable operating roles.
Explore Govern
Test assurance as systems change.
Bring repeatable control validation into the delivery path before higher-risk changes move forward.
Explore CI Gate
Keep authority visible in operation.
Support runtime review and response around sensitive tools, actions, and business workflows.
Explore Runtime Guard
Explore only the service relevant to your immediate risk.
Plan and engineer enterprise AI workflows with clear security boundaries, operating controls, and production-readiness criteria.
Test AI agents and autonomous workflows for prompt injection, tool misuse, data exposure, control bypass, and unsafe business actions.
Assess AI agent permissions, tools, memory, context, identity, approvals, and runtime controls before business-critical deployment.
Engineer security-conscious AI applications, integrations, automation, and remediation for enterprise environments.
Translate enterprise AI risk into accountable governance, operational evidence, monitoring, and compliance-ready review practices.
Orbyntis work starts by making the agent boundary explicit, then turns risk into engineered controls, validation evidence, and operating ownership.
Define the agent, users, identities, data, tools, approvals, and business actions in scope.
Connect prompt, context, identity, tool, and approval risks to business impact.
Place deterministic checks around sensitive actions instead of relying only on model behavior.
Exercise realistic failure paths and confirm controls hold under adversarial or degraded conditions.
Keep ownership, logging, containment, and reassessment tied to material workflow changes.
Use these evergreen guides to understand autonomous AI threats, agent security decisions, enterprise patterns, and common assurance questions.
A practical hub for authority, tools, identity, context, controls, and runtime evidence.
Threat families for agentic workflows, mapped to business impact and control questions.
Server, tool, testing, prompt injection, and data exposure guidance for MCP-connected agents.
Retrieval testing, prompt injection, and data leakage guidance for enterprise AI systems.
Short answers to common questions about agent security, red teaming, approvals, and evidence.
Anonymous patterns from AI risk, red teaming, governance, and assurance work.
Start with a focused briefing. Leave with a clearer assurance path.
Request a Briefing